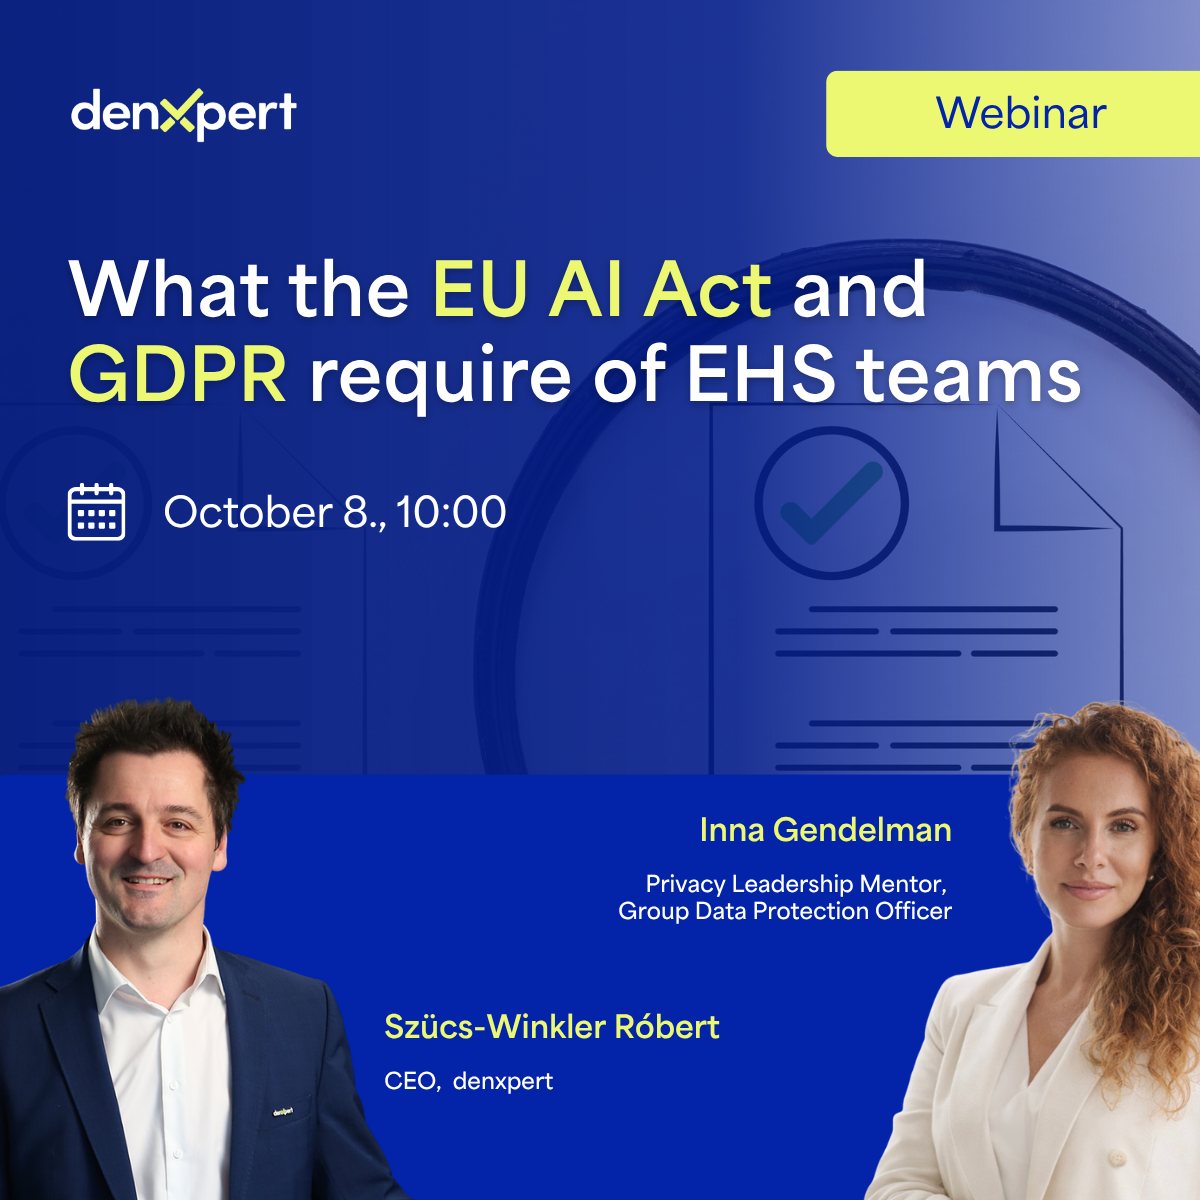
What the EU AI Act and GDPR require of EHS teams
Using AI responsibly in EHS: what applies now, and how to prepare for it

- GDPR requirements in daily EHS work: Translate transparency, data minimisation, access control, retention, accountability and individual rights into practical EHS controls.
- AI Act risk classification: Distinguish between limited-risk use cases, potentially high-risk worker-related systems and practices that may be prohibited.
- Clear internal responsibilities: Understand how EHS, Legal, the DPO, IT Security, HR and employee representatives contribute to a compliant process.
- AI in EHS: Identify AI already embedded in EHS software as well as the use of general-purpose AI outside approved systems.
- denxpert enhanced with AI: What the platform does today, and what is coming next.

The regulatory picture: GDPR, the EU AI Act and the EHS context
GDPR applies whenever an EHS process uses personal data. Depending on the use case, this may include employment data, health information, incident reports, witness statements, training records, location data, photographs or information generated by sensors and monitoring tools.
The EU AI Act adds a separate, risk-based layer. Many supportive uses of AI will not qualify as high-risk. However, AI that monitors or evaluates workers, influences working conditions, allocates tasks based on personal characteristics or acts as a safety component of a regulated product may require closer assessment. Certain uses, including emotion recognition in the workplace, may be prohibited except under narrow conditions.
For EHS teams, the practical challenge is therefore not simply determining whether a product contains AI. They need to understand the purpose, the affected people, the data involved and how the output influences real decisions.
The focus is not on turning EHS professionals into lawyers, but on helping them ask the right questions, involve the right experts and design processes that can withstand legal and operational scrutiny.
AI in denxpert
At the end of the session we will show how this works in practice. denxpert AI runs in a closed environment on our own AI setup, so your data stays inside your denxpert system, and answers draw on the EHS knowledge base we have been building for over 20 years.
What you will take away
Participants will leave with a practical framework for reviewing EHS processes involving personal data and AI. You will learn how to map the relevant data flow, identify the questions that require support from Legal, the DPO or IT Security, recognise potentially sensitive AI use cases and assess whether your existing documentation and controls are sufficient.
The session concludes with an EHS legal challenge checklist that teams can use when introducing new software, activating AI functionality or reviewing existing processes.
Who should join
EHS leaders and managers, compliance professionals, Data Protection Officers, privacy and employment-law specialists, HR professionals, IT and information-security decision-makers, AI governance teams and organisations introducing or operating AI-enabled EHS systems.
Our Experts